mvdmio · Compliance
ISO 27001 Statement of Applicability template
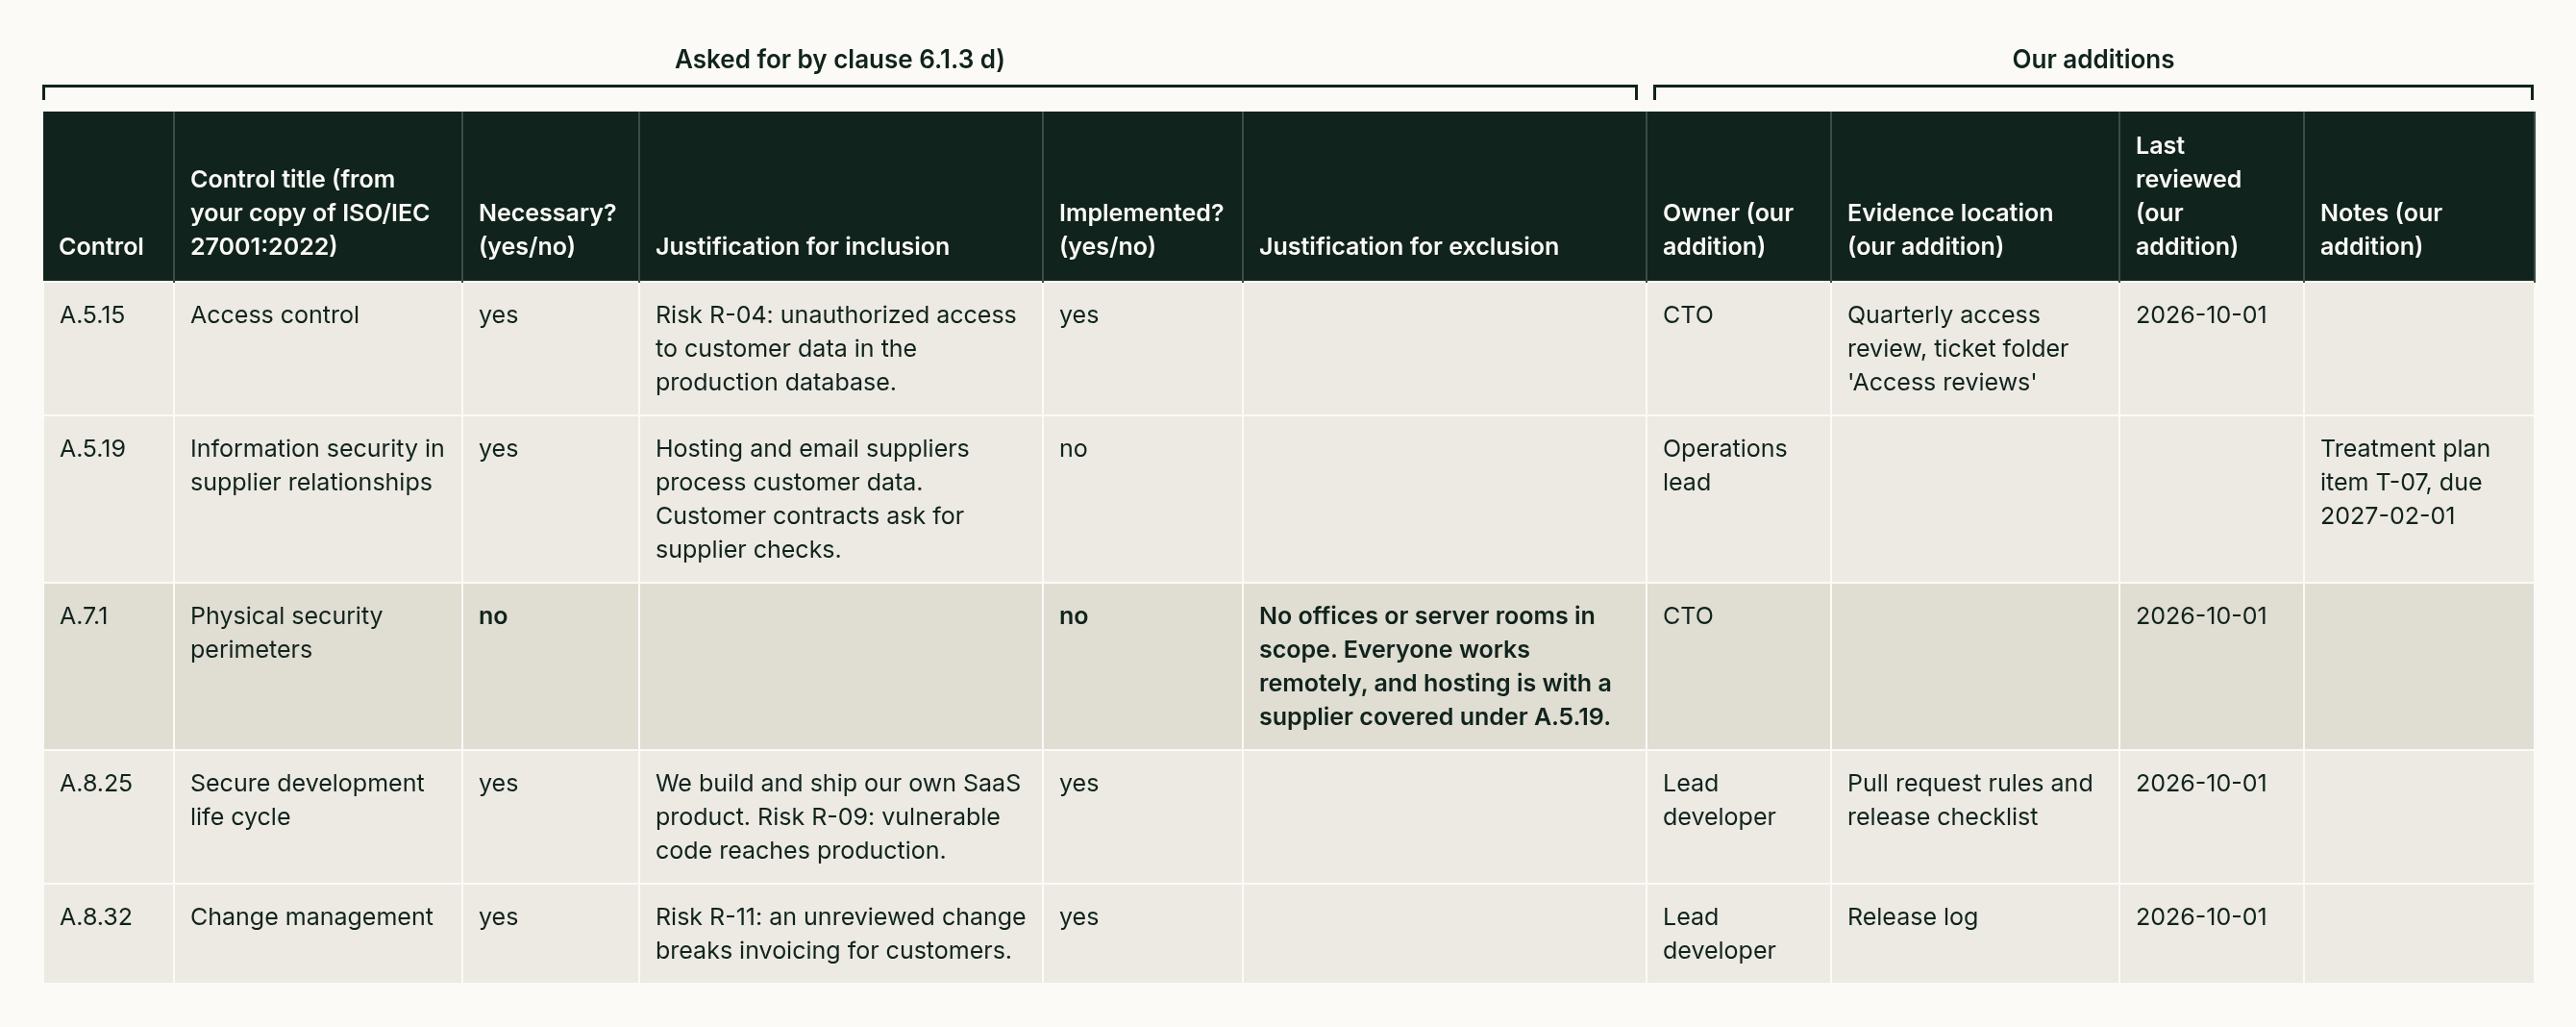
A customer asks for your ISO 27001 Statement of Applicability, and you don't have one yet. This template gives you the columns clause 6.1.3 d) asks for, with a few example rows for a fictional SaaS company.
Leave your email address below and Michiel van der Meer, who builds Compliance, emails you the template as an Excel file and a CSV.
What's in the template
The sheet has one row per control. Columns A to F follow clause 6.1.3 d) of ISO/IEC 27001:2022:
- Control, the Annex A number or your own control number.
- Control title.
- Necessary, yes or no.
- Justification for inclusion.
- Implemented, yes or no.
- Justification for exclusion.
Columns G to J are our additions. The standard doesn't ask for them, but they make the next review shorter:
- Owner, the person who keeps the control running.
- Evidence location, where someone can see that the control works.
- Last reviewed, the date someone last checked the row.
- Notes, for example the item in your risk treatment plan.
The example rows use the official control names from ISO/IEC 27001:2022 Annex A, such as A.5.15 Access control and A.7.1 Physical security perimeters. A.7.1 is excluded in the example, because the fictional company has no offices or server rooms in scope. The file holds no other ISO text. For the official text, get ISO/IEC 27001:2022 and ISO/IEC 27002:2022 from your national standards body.
A "How to use" sheet explains each column in a few lines.
Who it's for
It's for the founder, CTO or developer at a software company whose customer has just asked for ISO 27001 in a security review. You may not be certified yet, or you may be starting your first information security management system (ISMS). Either way, you need to know what this document looks like before you write one.
The Statement of Applicability follows from your risk assessment. It doesn't replace it. Start from the risks you treat, then go through Annex A and write one reason on every row. "N/A" on its own is not a reason.
Get the template
Michiel emails the template to the address you give. Name and company are optional.
You get the template by email. You can ask Michiel to stop or to delete your details at michiel@mvdm.io.
Run applicability in Compliance
In Compliance you decide applicability per Annex A control, with a justification for each exclusion. On ISO 27001 you do that on the Applicability (SoA) tab.
Each control there is Applicable, Excluded or Not yet reviewed. Opening a control you haven't reviewed doesn't decide anything. When you choose Mark excluded, Compliance asks for the justification, and it shows on the control's Details page. Each control has its official control name, with our own plain-language guidance under it. For the official text, use your copy of ISO/IEC 27002.
The same Applicability page exists for regulations with optional requirements, such as the EU GDPR and the EU AI Act. There the page is called Applicability. "(SoA)" appears only on certification standards such as ISO 27001.
The AI assistant can mark a control applicable or excluded for you, and it gives a justification for an exclusion. Treat it as advice. You make the call.
Compliance has no field for the justification for including a control. Keep that part in your own document, such as this template.
Used at Jewel Software, where Michiel van der Meer is Tech Lead. He built Compliance after taking over an ISMS there and seeing how much hand-work it took.
Try Compliance for 30 days without a credit card. The trial gives you full access to every framework. The AI assistant is not part of the trial unless you buy AI credits.
Questions about the Statement of Applicability
Does ISO 27001 require a Statement of Applicability?
Yes. Clause 6.1.3 d) of ISO/IEC 27001:2022 asks you to produce one, as part of risk treatment.
Can I exclude an Annex A control?
Yes, with a reason. The clause asks for the justification for excluding any Annex A control. Clause 6.1.3 c) also asks you to check that no necessary control is left out.
Does the template include the text of ISO 27001?
The example rows use the official control names from Annex A. The template holds no other ISO text. Get ISO/IEC 27001:2022 and ISO/IEC 27002:2022 from your national standards body for the official text.
How do I get the template?
Fill in the form with your email address. Michiel emails you the template as an Excel file and a CSV.
What happens with my email address?
It's kept in mvdm.io Sales with your name and company if you give them, and the page and campaign that brought you. It's used only to email you about compliance, under the privacy notice. Ask michiel@mvdm.io to stop or to delete your details.
Can Compliance give me a Statement of Applicability?
In Compliance you decide applicability per Annex A control, with a justification for each exclusion. The other items clause 6.1.3 d) asks for, such as the justification for including a control, you write in your own document, for example this template.
Does this template make us compliant or certified?
No. A certification body audits your ISMS against ISO 27001 and issues the certificate. The template helps you write one of the documents the standard asks for.